Management Summary
ReplicatsAI contacted Sayfer to perform a security audit on their smart contracts in 09/2025
This report documents the research carried out by Sayfer targeting the selected resources defined under the research scope. Particularly, this report displays the security posture review for ReplicatsAI’s smart contracts.
Over the research period of 2 weeks, we discovered 8 vulnerabilities in the contracts.
Several fixes should be implemented following the report, to ensure the system’s security posture is competent.
After a review by the Sayfer team, we certify that all the security issues mentioned in this report have been addressed by the ReplicatsAI team.
Risk Methodology
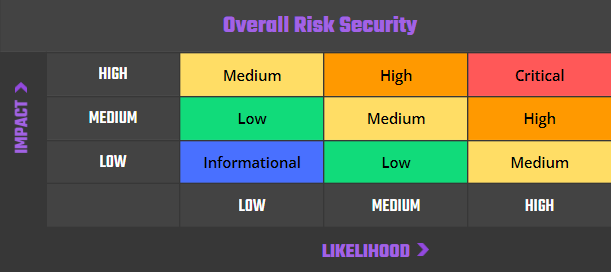
At Sayfer, we are committed to delivering the highest quality smart contract audits to our clients. That’s why we have implemented a comprehensive risk assessment model to evaluate the severity of our findings and provide our clients with the best possible recommendations for mitigation.
Our risk assessment model is based on two key factors: IMPACT and LIKELIHOOD. Impact refers to the potential harm that could result from an issue, such as financial loss, reputational damage, or a non-operational system. Likelihood refers to the probability that an issue will occur, taking into account factors such as the complexity of the contract and the number of potential attackers.
By combining these two factors, we can create a comprehensive understanding of the risk posed by a particular issue and provide our clients with a clear and actionable assessment of the severity of the issue. This approach allows us to prioritize our recommendations and ensure that our clients receive the best possible advice on how to protect their smart contracts.
Risk is defined as follows:
Vulnerabilities by Risk
High – Direct threat to key business processes.
Medium – Indirect threat to key business processes or partial threat to business processes.
Low – No direct threat exists. The vulnerability may be exploited using other vulnerabilities.
Informational – This finding does not indicate vulnerability, but states a comment that notifies about design flaws and improper implementation that might cause a problem in the long run.
| Severity | # of issues |
|---|---|
| Low | 2 |
| Medium | 4 |
| High | 1 |
| Critical | 0 |
| Informational | 1 |
Approach
Introduction
ReplicatsAI contacted Sayfer to perform a security audit on their smart contracts.
This report documents the research carried out by Sayfer targeting the selected resources defined under the research scope. Particularly, this report displays the security posture review for the aforementioned contracts.
Scope Overview
Together with the client team we defined the following contract as the scope of the project
| Contract | Sha-256 |
| CustomPriceFeed.sol | fbe78d8c523b864df00850c0ac9f545bcadd25b958b90a3fd468e4aba6a641f8 |
| Vault.sol | b032c84f42d1ae651aceb99061241670421ad9b86c07b7efef355bb19bcf7e33 |
| VaultFactory.sol | b6c5175042ddb1560315d03dde2be5f04f42c5e2305e66c1dddba642fb28d184 |
Our tests were performed from 07/09/2025 to 21/09/2025.
Scope Validation
We began by ensuring that the scope defined to us by the client was technically logical.
Deciding what scope is right for a given system is part of the initial discussion.
Threat Model
We defined that the largest current threat to the system is the ability of malicious users to steal funds from the contract.
Security Evaluation
The following test cases were the guideline while auditing the system. This checklist is a modified version of the SCSVS v1.2, with improved grammar, clarity, conciseness, and additional criteria. Where there is a gap in the numbering, an original criterion was removed. Criteria that are marked with an asterisk were added by us.
Architecture, Design and Threat Modeling
| Architecture, Design and Threat Modeling | Test Name |
| G1.2 | Every introduced design change is preceded by threat modeling. |
| G1.3 | The documentation clearly and precisely defines all trust boundaries in the contract (trusted relations with other contracts and significant data flows). |
| G1.4 | The SCSVS, security requirements or policy is available to all developers and testers. |
| G1.5 | The events for the (state changing/crucial for business) operations are defined. |
| G1.6 | The project includes a mechanism that can temporarily stop sensitive functionalities in case of an attack. This mechanism should not block users’ access to their assets (e.g. tokens). |
| G1.7 | The amount of unused cryptocurrencies kept on the contract is controlled and at the minimum acceptable level so as not to become a potential target of an attack. |
| G1.8 | If any ‘catch-all’ CPI handler (e.g., Anchor’s default route) is publicly reachable, it is included in the threat model. |
| G1.9 | Business logic is consistent. Important changes in the logic should be applied in all contracts. |
| G1.10 | Automatic code analysis tools are employed to detect vulnerabilities. |
| G1.11 | The program is compiled with the latest stable Solana SDK version (anchor + solana-program) |
| G1.12 | When using an external implementation of a contract, the most recent version is used. |
| G1.13 | When functions are overridden to extend functionality, the super keyword is used to maintain previous functionality. |
| G1.14 | The order of inheritance is carefully specified. |
| G1.15 | There is a component that monitors contract activity using events. |
| G1.16 | The threat model includes whale transactions. |
| G1.17 | The leakage of one private key does not compromise the security of the entire project. |
Policies and Procedures
| Policies and Procedures | Test Name |
| G2.2 | The system’s security is under constant monitoring (e.g. the expected level of funds). |
| G2.3 | There is a policy to track new security vulnerabilities and to update libraries to the latest secure version. |
| G2.4 | The security department can be publicly contacted and that the procedure for handling reported bugs (e.g., thorough bug bounty) is well-defined. |
| G2.5 | The process of adding new components to the system is well defined. |
| G2.6 | The process of major system changes involves threat modeling by an external company. |
| G2.7 | The process of adding and updating components to the system includes a security audit by an external company. |
| G2.8 | In the event of a hack, there’s a clear and well known mitigation procedure in place. |
| G2.9 | The procedure in the event of a hack clearly defines which persons are to execute the required actions. |
| G2.10 | The procedure includes alarming other projects about the hack through trusted channels. |
| G2.11 | A private key leak mitigation procedure is defined. |
Upgradability
| Upgradability | Test Name |
| G3.2 | Before upgrading, an emulation is made in a fork of the main network and everything works as expected on the local copy. |
| G3.3 | The upgrade process is executed by a multisig contract where more than one person must approve the operation. |
| G3.4 | Timelocks are used for important operations so that the users have time to observe upcoming changes (please note that removing potential vulnerabilities in this case may be more difficult). |
| G3.5 | initialize() can only be called once. |
| G3.6 | initialize() can only be called by an authorized role through Anchor access-control macros (e.g., #[access_control(admin_only)]). |
| G3.7 | The update process is done in a single transaction so that no one can front-run it. |
| G3.8 | Upgradeable contracts have reserved gap on slots to prevent overwriting. |
| G3.9 | The number of reserved (as a gap) slots has been reduced appropriately if new variables have been added. |
| G3.10 | There are no changes in the order in which the contract state variables are declared, nor their types. |
| G3.11 | New values returned by the functions are the same as in previous versions of the contract (e.g. owner(), balanceOf(address)). |
| G3.12 | The implementation is initialized. |
| G3.13 | The implementation can’t be destroyed. |
Business Logic
| Business Logic | Test Name |
| G4.2 | The contract logic and protocol parameters implementation corresponds to the documentation. |
| G4.3 | The business logic proceeds in a sequential step order and it is not possible to skip steps or to do it in a different order than designed. |
| G4.4 | The contract has correctly enforced business limits. |
| G4.5 | The business logic does not rely on the values retrieved from untrusted contracts (especially when there are multiple calls to the same contract in a single flow). |
| G4.6 | The business logic does not rely on the contract’s balance (e.g., balance == 0). |
| G4.7 | Sensitive operations do not depend on block data (e.g., block hash, timestamp). |
| G4.8 | The contract uses mechanisms that mitigate transaction-ordering (front-running) attacks (e.g. pre-commit schemes). |
| G4.9 | The contract does not send funds automatically, but lets users withdraw funds in separate transactions instead. |
Access Control
| Access Control | Test Name |
| G5.2 | The principle of the least privilege is upheld. Other contracts should only be able to access functions and data for which they possess specific authorization. |
| G5.3 | New contracts with access to the audited contract adhere to the principle of minimum rights by default. Contracts should have a minimal or no permissions until access to the new features is explicitly granted. |
| G5.4 | The creator of the contract complies with the principle of the least privilege and their rights strictly follow those outlined in the documentation. |
| G5.5 | The contract enforces the access control rules specified in a trusted contract, especially if the dApp client-side access control is present and could be bypassed. |
| G5.6 | Calls to external contracts are only allowed if necessary. |
| G5.7 | Modifier code is clear and simple. The logic should not contain external calls to untrusted contracts. |
| G5.8 | All user and data attributes used by access controls are kept in trusted contracts and cannot be manipulated by other contracts unless specifically authorized. |
| G5.9 | the access controls fail securely, including when a revert occurs. |
| G5.10 | If the input (function parameters) is validated, the positive validation approach (whitelisting) is used where possible. |
Communication
| Communication | Test Name |
| G6.2 | Libraries that are not part of the application (but the smart contract relies on to operate) are identified. |
| G6.3 | Cross-program invocations (CPIs) to untrusted programs are prohibited unless account constraints are strictly validated. |
| G6.4 | Third-party programs do not override error handling or message passing in a way that obscures on-chain logs. |
| G6.5 | CPIs are validated against expected program IDs and account constraints before invocation. |
| G6.6 | The result of each CPI (including returned data) is checked and errors are bubbled up. |
| G6.7 | Program verifies the signer / writable account metas supplied to each instruction and never relies on sysvar::instructions order alone. |
Arithmetic
| Arithmetic | Test Name |
| G7.2 | All arithmetic respects Rust’s checked/unwrapped semantics, and explicit panics are avoided. |
| G7.3 | Any unchecked {} arithmetic blocks in Rust do not introduce wrapping or panic conditions. |
| G7.4 | Extreme values (e.g. maximum and minimum values of the variable type) are considered and do not change the logic flow of the contract. |
| G7.5 | Non-strict inequality is used for balance equality. |
| G7.6 | Correct orders of magnitude are used in the calculations. |
| G7.7 | In calculations, multiplication is performed before division for accuracy. |
| G7.8 | The contract does not assume fixed-point precision and uses a multiplier or store both the numerator and denominator. |
Denial of Service
| Denial of Service | Test Name |
| G8.2 | The contract does not iterate over unbound loops. |
| G8.3 | The business logic isn’t blocked if an actor (e.g. contract, account, oracle) is absent. |
| G8.4 | The business logic does not disincentivize users to use contracts (e.g. the cost of transaction is higher than the profit). |
| G8.5 | Expressions of functions assert or require have a passing variant. |
| G8.6 | There are no costly operations in a loop. |
| G8.7 | There are no calls to untrusted contracts in a loop. |
| G8.8 | If there is a possibility of suspending the operation of the contract, it is also possible to resume it. |
| G8.9 | If whitelists and blacklists are used, they do not interfere with normal operation of the system. |
| G8.10 | No DoS via compute unit exhaustion, account size overflow, or account lock contention. |
Blockchain Data
| Blockchain Data | Test Name |
| G9.2 | Any saved data in contracts is not considered secure or private (even private variables). |
| G9.3 | No confidential data is stored in the blockchain (passwords, personal data, token etc.). |
| G9.4 | Contracts do not use string literals as keys for mappings. Global constants are used instead to prevent Homoglyph attack. |
| G9.5 | Contract does not trivially generate pseudorandom numbers based on the information from blockchain (e.g. seeding with the block number). |
Gas Usage and Limitations
| Compute-Unit Usage and Limitations | Test Name |
| G10.2 | Compute-unit usage is anticipated, defined and has clear limitations that cannot be exceeded. |
| G10.3 | Program logic does not depend on hard-coded compute budgets or lamport fee assumptions. |
Clarity and Readability
| Clarity and Readability | Test Name |
| G11.2 | The logic is clear and modularized in multiple simple contracts and functions. |
| G11.3 | Each contract has a short 1-2 sentence comment that explains its purpose and functionality. |
| G11.4 | Off-the-shelf implementations are used, this is made clear in comment. If these implementations have been modified, the modifications are noted throughout the contract. |
| G11.5 | The inheritance order is taken into account in contracts that use multiple inheritance and shadow functions. |
| G11.6 | Where possible, contracts use existing tested code (e.g. token contracts or mechanisms like ownable) instead of implementing their own. |
| G11.7 | Consistent naming patterns are followed throughout the project. |
| G11.8 | Variables have distinctive names. |
| G11.9 | All storage variables are initialized. |
| G11.10 | Functions with specified return type return a value of that type. |
| G11.11 | All functions and variables are used. |
| G11.12 | require is used instead of revert in if statements. |
| G11.13 | The assert function is used to test for internal errors and the require function is used to ensure a valid condition in input from users and external contracts. |
| G11.14 | Assembly code is only used if necessary. |
Test Coverage
| Test Coverage | Test Name |
| G12.2 | Abuse narratives detailed in the threat model are covered by unit tests. |
| G12.3 | Sensitive functions in verified contracts are covered with tests in the development phase. |
| G12.4 | Implementation of verified contracts has been checked for security vulnerabilities using both static and dynamic analysis. |
| G12.5 | Contract specification has been formally verified. |
| G12.6 | The specification and results of the formal verification is included in the documentation. |
Decentralized Finance
| Decentralized Finance | Test Name |
| G14.1 | The lender’s contract does not assume its balance (used to confirm loan repayment) to be changed only with its own functions. |
| G14.2 | Functions that move lender balances are protected against CPI chaining that could manipulate balances during flash-loan-style operations on Solana. |
| G14.3 | Flash loan functions can only call predefined functions on the receiving contract. If it is possible, define a trusted subset of contracts to be called. Usually, the sending (borrowing) contract is the one to be called back. |
| G14.4 | If it includes potentially dangerous operations (e.g. sending back more SOL/SPL tokens than borrowed), the receiver’s function that handles borrowed SOL or tokens can be called only by the pool and within a process initiated by the receiving contract’s owner or another trusted source (e.g. multisig). |
| G14.5 | Calculations of liquidity pool share are performed with the highest possible precision (e.g. if the contribution is calculated for SOL it should be done with 9 digit precision – for lamports). The dividend must be multiplied by the 10 to the power of the number of decimal digits (e.g. dividend * 10^9 / divisor). |
| G14.6 | Rewards cannot be calculated and distributed within the same function call that deposits tokens (it should also be defined as non-re-entrant). This protects from momentary fluctuations in shares. |
| G14.7 | Governance contracts are protected from flash loan attacks. One possible mitigation technique is to require the process of depositing governance tokens and proposing a change to be executed in different transactions included in different blocks. |
| G14.8 | When using on-chain oracles, contracts are able to pause operations based on the oracles’ result (in case of a compromised oracle). |
| G14.9 | External contracts (even trusted ones) that are allowed to change the attributes of a project contract (e.g. token price) have the following limitations implemented: thresholds for the change (e.g. no more/less than 5%) and a limit of updates (e.g. one update per day). |
| G14.10 | Contract attributes that can be updated by the external contracts (even trusted ones) are monitored (e.g. using events) and an incident response procedure is implemented (e.g. during an ongoing attack). |
| G14.11 | Complex math operations that consist of both multiplication and division operations first perform multiplications and then division. |
| G14.12 | When calculating swap prices (e.g. SOL ↔ SPL token) the numerator and denominator are multiplied by reserves, as done in constant-product AMMs on Solana (e.g., Orca). |
Security Assessment Findings
Fees are under Agent Control
| ID | SAY-01 |
| Status | Fixed |
| Risk | High |
| Business Impact | A malicious or misconfigured agent can set an extreme fee and, via payFee, rapidly drain RCAT from the vault to the treasury and destabilize operations. |
| Location | – Vault.sol; setFeePerMin(address, address) |
Description
setFeePerMin(address, address) allows the agent to update the feePerMin state parameter. This parameter defines the amount of fee being paid in payFee(address), which is also under the control of the agent. This incentives the agent to set the fee to the maximum allowed value in order to maximize profits.
- Vault.sol:471-475
function setFeePerMin(uint256 _feePerMin) external onlyAgent {
    require(_feePerMin > 0, "Vault Contract: fee > 0");
    require(_feePerMin = 10_000_000, "Vault Contract: fee too large");
    feePerMin = _feePerMin;
}
Mitigation
Review the access control scheme and the logic behind it and make sure to remove any perverse incentive.
No Operation Whitelist in trade(…)
| ID | SAY-02 |
| Status | Fixed |
| Risk | Medium |
| Business Impact | Allowing agents to supply arbitrary call data significantly broadens callable behavior and can trigger unexpected state changes or fund loss beyond intended swap paths. |
| Location | – Vault.sol; trade(address, address, address, uint256, bytes) |
Description
trade(…) allows the agent to perform any swap call on an approved router, but does not define a whitelist for allowed functions. Thus, the broad range of functions to be called creates an uncertain and undefined potential attack surface. Moreover, there is no security control in place to restrict what type of router can be whitelisted within the protocol. So it is uncertain whether Uniswap v2, Uniswap v3 or any other router will be used, e.g. a router which allows to make callbacks.
Such a permissive approach can lead to multiple various potential issues and exploits. Nevertheless, here too the slippage protection implemented in the function restricts the possible scope of abuse.
Mitigation
Consider implementing more strict rules regarding the list of operations that could be triggered by the trade agent.
Router Allowance Can’t Be Decreased
| ID | SAY-03 |
| Status | Fixed |
| Risk | Medium |
| Business Impact | Excess allowances persist indefinitely, exposing tokens to misuse if the router or agent is compromised until router access is changed. |
| Location | – Vault.sol; approveTrade(address, address, uint256) |
Description
approveTrade(address, address, uint256) allows the agent to increase the allowance for a particular token and router. However, there is no function to revoke the granted allowance. Thus, an abusive agent can set any allowance and abuse it until the access is revoked.
Mitigation
It is recommended to implement a function that enables the owner to decrease or revoke router allowances.
payFee(address) is Vulnerable to DOS Attacks
| ID | SAY-04 |
| Status | Fixed |
| Risk | Medium |
| Business Impact | Insufficient RCAT causes perpetual payFee reverts while debt grows. |
| Location | – Vault.sol; payFee(address) |
Description
payFee(address) calculates the amount of RCAT tokens required to be transferred to the treasury address. However, there is no possibility to transfer only part of the tokens owed to the treasury. Thus, the success of the transfer relies only on the RCAT token contract’s balance. If the balance is insufficient, the amount of the tokens to be paid over time can inflate, and can be too high to be ever paid, even when supplying the contract with additional RCAT amount
Mitigation
It is recommended to review the implementation and consider robust accounting that allows end users to transfer a particular amount of fees on demand.
No Price Staleness Checks
| ID | SAY-05 |
| Status | Acknowledged |
| Risk | Medium |
| Business Impact | Stale prices can distort TVL, slippage, and exposure checks, leading to mispriced trades or breached risk limits. |
| Location | – Vault.sol; getTokenPriceUsd1e18(address) |
Description
getTokenPriceUsd1e18(address) makes use of the price-feed price as it is without checking the price staleness. Such implementation may lead to use of third party price-feed with obsolete and incorrect price. Finally, this can affect the final protocol accounting in terms of TVL.
- Vault.sol:111-124
function getTokenPriceUsd1e18(address token) public view returns
(uint256) {
    if (token = USDC) return 1e18;
    address feedAddr = priceFeeds[token];
    require(feedAddr = address(0), "Vault Contract: no price feed");
    (, int256 price, , , ) = AggregatorV3Interface(feedAddr)
        .latestRoundData();
    require(price > 0, "Vault Contract: bad price");
    uint8 pdec = AggregatorV3Interface(feedAddr).decimals();
    if (pdec < 18) return uint256(price) * (10 * (18 - pdec));
    if (pdec > 18) return uint256(price) / (10 * (pdec - 18));
    return uint256(price);
}
Mitigation
It is recommended to save a heartbeat value for each price feed and compare the price staleness with the heartbeat. Whenever the price is stale it should be rejected by the protocol.
getUserVaults(…) May Return an Incorrect Value
| ID | SAY-06 |
| Status | Acknowledged |
| Risk | Low |
| Business Impact | UIs or tooling relying on this view will show stale ownership upon transferral of vault ownership, causing confusion and potential mis-routing of actions. |
| Location | – VaultFactory.sol; getUserVaults(address) |
Description
getUserVaults(address) returns all vaults belonging to a single user. However, vault owners can transfer their ownership to another address. Whenever transferral occurs, the records in this collection become obsolete.
- VaultFactory.sol:94-98
function getUserVaults(
    address user
) external view returns (address[] memory) {
    return userVaults[user];
}
Mitigation
If this function is essential, it is recommended to implement a robust update mechanism that will notify the factory about ownership transferral.
One-step ownership transfer
| ID | SAY-07 |
| Status | Acknowledged |
| Risk | Low |
| Business Impact | Passing in a wrong address when transferring the ownership will result in the irrevocable loss of the ownership role. |
| Location | – CustomPriceFeed.sol – Vault.sol |
Description
transferOwnership(address) provided by OpenZeppelin’s Ownable immediately sets the new owner to the passed address, without requiring a confirmation from this account / contract. If a wrong address is passed, the Owner role will be instantly and irrecoverably lost.
Mitigation
To avoid errors when performing an ownership transfer, it is recommended to implement a two-step transfer. The current owner should only be able to set a new pending owner. This address then needs to accept the ownership by calling a dedicated function
An off the shelf solution, Ownable2Step, is also offered by OpenZeppelin.
Redundant Parameter
| ID | SAY-08 |
| Status | Acknowledged |
| Risk | Informational |
| Business Impact | Redundant parameters increase gas usage without enhancing functionality or safety. |
| Location | – Vault.sol; deposit(address, uin256) |
Description
deposit(address, uin256) accepts a token parameter, but then enforces that the deposit token must be USDC with an assertion. Thus, this appears to be redundant and therefore results in Gas overconsumption.
- Vault.sol:188-192
function deposit(
    address token,
    uint256 amount
) external onlyOwner nonReentrant {
    require(token = USDC, "Vault Contract: only USDC");
                                    ...
}
Mitigation
Either remove the redundant parameter, or the assertion that contradicts it.