Management Summary
LeapWallet contacted Sayfer Security in order to perform a complete audit on their Snap in 08/2023.
Before assessing the above services, we held a kickoff meeting with the LeapWallet Snap technical team and received an overview of the system and the goals for this research.
Over the research period of 4 weeks, we discovered 7 vulnerabilities in the system.
Several fixes should be implemented following the report, but the system’s security posture is competent.
Risk Methodology
At Sayfer, we are committed to delivering the highest quality penetration testing to our clients. That’s why we have implemented a comprehensive risk assessment model to evaluate the severity of our findings and provide our clients with the best possible recommendations for mitigation.
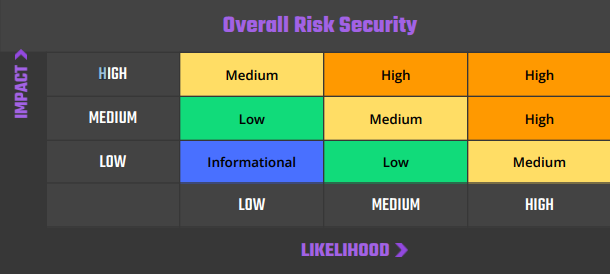
Our risk assessment model is based on two key factors: IMPACT and LIKELIHOOD. Impact refers to the potential harm that could result from an issue, such as financial loss, reputational damage, or a non-operational system. Likelihood refers to the probability that an issue will occur, taking into account factors such as the complexity of the attack and the number of potential attackers.
By combining these two factors, we can create a comprehensive understanding of the risk posed by a particular issue and provide our clients with a clear and actionable assessment of the severity of the issue. This approach allows us to prioritize our recommendations and ensure that our clients receive the best possible advice on how to protect their business.
Risk is defined as follows:
Vulnerabilities by Risk
High – Direct threat to key business processes.
Medium – Indirect threat to key business processes or partial threat to business processes.
Low – No direct threat exists. The vulnerability may be exploited using other vulnerabilities.
Informational – This finding does not indicate vulnerability, but states a comment that notifies about design flaws and improper implementation that might cause a problem in the long run.
| Severity | # of issues |
|---|---|
| High | 0 |
| Medium | 1 |
| Low | 2 |
| Informational | 4 |
Approach
Introduction
LeapWallet Snap contacted Sayfer to perform complete black box penetration testing on the MetaMask Snap.
This report documents the research carried out by Sayfer targeting the selected resources defined under the research scope. Particularly, this report displays the security posture review for the Snap application and its surrounding infrastructure and process implementations.
Scope Overview
During our first meeting and after understanding the company’s needs, we defined the application’s scope that resides at the following URLs as the scope of the project:
- LeapWallet Snap
Audit commit: ea93aaf116b89539d434b922e2d315304faf4e37
Fixes commit: c9ed0cef9b345e01acc628decb7dac24baceb275
Our tests were performed from 01/08/2023 to 30/08/2023.
Scope Validation
We began by ensuring that the scope defined to us by the client was technically logical. Deciding what scope is right for a given system is part of the initial discussion. Getting the scope right is key to deriving maximum business value from the research.
Threat Model
During our kickoff meetings with the client, we defined the most important assets the application possesses.
Security Evaluation Methodology
Sayfer uses OWASP WSTG as our technical standard when reviewing web applications. After gaining a thorough understanding of the system we decided which OWASP tests are required to evaluate the system.
Security Assessment
After understanding and defining the scope, performing threat modeling, and evaluating the correct tests required in order to fully check the application for security flaws, we performed our security assessment.
Tools Used
During the test, we used multiple automated tools in addition to our manual tests, including the following: Burp Suite Professional, Web browser, DevTools, Nmap, Metasploit, SQLmap, Nessus, Shodan, Hydra, John the Ripper and wafw00f.
Issue Table Description
Issue title
| ID | The OWASP ID of the issue. Additional tests that we conduct and are not included in the OWASP table will have Sayfer ID. Example ID: WSTG-INFO-002 WSTG – Web Security Test Guide. INFO – A shorthand for the topic to which the issue belongs. 002 – Issue number. |
| Risk | Represents the risk factor of the issue. For further description refer to the Vulnerabilities by Risk section. |
| Required Skill | Describes the skill level required to conduct successful exploitation. The lower the skill level the easier the exploitation process. |
| OWASP Reference |
A link to the relevant OWASP page for further knowledge. |
| Location | The URL in which this issue was detected. Issues with no location have no particular location and refer to the product as a whole. |
| Business Impact | The impact of the findings on the system. |
Description
Here we provide a brief description of the issue and how it formed, the steps we made to find or exploit it, along with proof of concept (if present), and how this issue can affect the product or its users.
Mitigation
Suggested resolving options for this issue and links to advised sites for further remediation.
Security Evaluation
The following tests were conducted while auditing the system
Information Gathering
| Information Gathering | Test Name |
| WSTG-INFO-01 | Conduct Search Engine Discovery Reconnaissance for Information Leakage |
| WSTG-INFO-02 | Fingerprint Web Server |
| WSTG-INFO-03 | Review Webserver Metafiles for Information Leakage |
| WSTG-INFO-04 | Enumerate Applications on Webserver |
| WSTG-INFO-05 | Review Webpage Content for Information Leakage |
| WSTG-INFO-06 | Identify application entry points |
| WSTG-INFO-07 | Map execution paths through application |
| WSTG-INFO-08 | Fingerprint Web Application Framework |
| WSTG-INFO-09 | Fingerprint Web Application |
| WSTG-INFO-10 | Map Application Architecture |
Configuration and Deploy Management Testing
| Configuration and Deploy Management Testing | Test Name |
| WSTG-CONF-01 | Test Network Infrastructure Configuration |
| WSTG-CONF-02 | Test Application Platform Configuration |
| WSTG-CONF-03 | Test File Extensions Handling for Sensitive Information |
| WSTG-CONF-04 | Review Old Backup and Unreferenced Files for Sensitive Information |
| WSTG-CONF-05 | Enumerate Infrastructure and Application Admin Interfaces |
| WSTG-CONF-06 | Test HTTP Methods |
| WSTG-CONF-07 | Test HTTP Strict Transport Security |
| WSTG-CONF-08 | Test RIA cross domain policy |
| WSTG-CONF-09 | Test File Permission |
| WSTG-CONF-10 | Test for Subdomain Takeover |
| WSTG-CONF-11 | Test Cloud Storage |
Identity Management Testing
| Identity Management Testing | Test Name |
| WSTG-IDNT-01 | Test Role Definitions |
| WSTG-IDNT-02 | Test User Registration Process |
| WSTG-IDNT-03 | Test Account Provisioning Process |
| WSTG-IDNT-04 | Testing for Account Enumeration and Guessable User Account |
| WSTG-IDNT-05 | Testing for Weak or unenforced username policy |
Authentication Testing
| Authentication Testing | Test Name |
| WSTG-ATHN-01 | Testing for Credentials Transported over an Encrypted Channel |
| WSTG-ATHN-02 | Testing for Default Credentials |
| WSTG-ATHN-03 | Testing for Weak Lock Out Mechanism |
| WSTG-ATHN-04 | Testing for Bypassing Authentication Schema |
| WSTG-ATHN-05 | Testing for Vulnerable Remember Password |
| WSTG-ATHN-06 | Testing for Browser Cache Weaknesses |
| WSTG-ATHN-07 | Testing for Weak Password Policy |
| WSTG-ATHN-08 | Testing for Weak Security Question Answer |
| WSTG-ATHN-09 | Testing for Weak Password Change or Reset Functionalities |
| WSTG-ATHN-10 | Testing for Weaker Authentication in Alternative Channel |
Authorization Testing
| Authorization Testing | Test Name |
| WSTG-ATHZ-01 | Testing Directory Traversal File Include |
| WSTG-ATHZ-02 | Testing for Bypassing Authorization Schema |
| WSTG-ATHZ-03 | Testing for Privilege Escalation |
| WSTG-ATHZ-04 | Testing for Insecure Direct Object References |
Session Management Testing
| Session Management Testing | Test Name |
| WSTG-SESS-01 | Testing for Session Management Schema |
| WSTG-SESS-02 | Testing for Cookies Attributes |
| WSTG-SESS-03 | Testing for Session Fixation |
| WSTG-SESS-04 | Testing for Exposed Session Variables |
| WSTG-SESS-05 | Testing for Cross Site Request Forgery |
| WSTG-SESS-06 | Testing for Logout Functionality |
| WSTG-SESS-07 | Testing Session Timeout |
| WSTG-SESS-08 | Testing for Session Puzzling |
| WSTG-SESS-09 | Testing for Session Hijacking |
Data Validation Testing
| Data Validation Testing | Test Name |
| WSTG-INPV-01 | Testing for Reflected Cross Site Scripting |
| WSTG-INPV-02 | Testing for Stored Cross Site Scripting |
| WSTG-INPV-03 | Testing for HTTP Verb Tampering |
| WSTG-INPV-04 | Testing for HTTP Parameter Pollution |
| WSTG-INPV-05 | Testing for SQL Injection |
| WSTG-INPV-06 | Testing for LDAP Injection |
| WSTG-INPV-07 | Testing for XML Injection |
| WSTG-INPV-08 | Testing for SSI Injection |
| WSTG-INPV-09 | Testing for XPath Injection |
| WSTG-INPV-10 | Testing for IMAP SMTP Injection |
| WSTG-INPV-11 | Testing for Code Injection |
| WSTG-INPV-12 | Testing for Command Injection |
| WSTG-INPV-13 | Testing for Format String Injection |
| WSTG-INPV-14 | Testing for Incubated Vulnerability |
| WSTG-INPV-15 | Testing for HTTP Splitting Smuggling |
| WSTG-INPV-16 | Testing for HTTP Incoming Requests |
| WSTG-INPV-17 | Testing for Host Header Injection |
| WSTG-INPV-18 | Testing for Server-side Template Injection |
| WSTG-INPV-19 | Testing for Server-Side Request Forgery |
Error Handling
| Error Handling | Test Name |
| WSTG-ERRH-01 | Testing for Improper Error Handling |
| WSTG-ERRH-02 | Testing for Stack Traces |
Cryptography
| Cryptography | Test Name |
| WSTG-CRYP-01 | Testing for Weak Transport Layer Security |
| WSTG-CRYP-02 | Testing for Padding Oracle |
| WSTG-CRYP-03 | Testing for Sensitive Information Sent via Unencrypted Channels |
| WSTG-CRYP-04 | Testing for Weak Encryption |
Business logic Testing
| Business logic Testing | Test Name |
| WSTG-BUSL-01 | Test Business Logic Data Validation |
| WSTG-BUSL-02 | Test Ability to Forge Requests |
| WSTG-BUSL-03 | Test Integrity Checks |
| WSTG-BUSL-04 | Test for Process Timing |
| WSTG-BUSL-05 | Test Number of Times a Function Can be Used Limits |
| WSTG-BUSL-06 | Testing for the Circumvention of Work Flows |
| WSTG-BUSL-07 | Test Defenses Against Application Mis-use |
| WSTG-BUSL-08 | Test Upload of Unexpected File Types |
| WSTG-BUSL-09 | Test Upload of Malicious Files |
Client Side Testing
| Client Side Testing | Test Name |
| WSTG-CLNT-01 | Testing for DOM-Based Cross Site Scripting |
| WSTG-CLNT-02 | Testing for JavaScript Execution |
| WSTG-CLNT-03 | Testing for HTML Injection |
| WSTG-CLNT-04 | Testing for Client Side URL Redirect |
| WSTG-CLNT-05 | Testing for CSS Injection |
| WSTG-CLNT-06 | Testing for Client Side Resource Manipulation |
| WSTG-CLNT-07 | Test Cross Origin Resource Sharing |
| WSTG-CLNT-08 | Testing for Cross Site Flashing |
| WSTG-CLNT-09 | Testing for Clickjacking |
| WSTG-CLNT-10 | Testing WebSockets |
| WSTG-CLNT-11 | Test Web Messaging |
| WSTG-CLNT-12 | Testing Browser Storage |
| WSTG-CLNT-13 | Testing for Cross Site Script Inclusion |
API Testing
| API Testing | Test Name |
| WSTG-APIT-01 | Testing GraphQL |
Security Assessment Findings
No Tests Found
| ID | SAY-01 |
| Status | Fixed |
| Risk | Medium |
| Location | Project-wide |
| Business Impact | Changing the functionality might break the business logic or add security vulnerability without the developer’s notice. |
Description
It was found that the snap lacks automated test coverage, particularly for critical paths in the application’s logic.
Automated testing is a key practice in modern software development, providing a way to quickly and reliably check that core features work as expected and that changes do not inadvertently introduce new bugs or vulnerabilities.
Mitigation
Add tests for basic functionality or important paths in the business logic.
formatAllowanceOption() is Missing a Default Case
| ID | SAY-02 |
| Status | Fixed |
| Risk | Low |
| Location | cosmos-metamask-snap-main/packages/snap/src/helpers/parser.ts |
| Business Impact | While forgoing a default case in a switch statement is not directly a security option, it is still considered a bad practice, since default is used to “catch” unexpected values. |
Description
It was found that in the formatAllowanceOption function, a switch statement is used without the default case.
Notice the lack of default case:
const formatAllowanceOption = (allowance:
parfait.cosmos.feegrant.grantAllowance['allowance']) => {
switch (allowance) {
case 'basic':
return 'Basic'
case 'periodic':
return 'Periodic'
case 'allowedMsg':
return 'Allowed Message'
}
}
Mitigation
Include a default case, possibly returning some error message.
Uncovered Cases in a Switch-Case Statement
| ID | SAY-03 |
| Status | Fixed |
| Risk | Low |
| Location | cosmos-metamask-snap-main/packages/snap/src/helpers/parser.ts:197,202 |
| Business Impact | Due to these omissions, if the message is of these types – their processing will be “silent”. The user will not receive any information about the operation. |
Description
It was noticed that for two cases in the switch inside getMessageDetails() i.e. GammSwapExactAndExit and GammSwapExactAndJoin, no return messages were provided.
Mitigation
Add appropriate return values for the two mentioned cases
tokenToString is Used Before Defined
| ID | SAY-04 |
| Status | Fixed |
| Risk | Informational |
| Location | cosmos-metamask-snap-main/packages/snap/src/helpers/parser.ts |
| Business Impact | While use before define is possible in JavaScript (and by extension, TypeScript), it is considered a bad practice that can reduce readability and maintainability. |
Description
While verifying the code with a linter, it was noted that the function token is used before it’s defined.
Notice how tokensToString calls tokenToString before it has been defined:
const tokensToString = (tokens: Token[]) => {
const traces = tokens.map((t) => tokenToString(t))
return traces.join(', ')
}
[...]
const tokenToString = (token: Token) => {
if (token?.denomination?.startsWith('u') ?? false) {
return `${token.quantity} ${token.denomination.slice(1)}`
}
return `${token?.quantity ?? ''} ${sliceAddress(token?.denomination ?? '')}`
}
Mitigation
Move tokenToString before tokensToString.
Unused Functions
| ID | SAY-05 |
| Status | Fixed |
| Risk | Informational |
| Location | cosmos-metamask-snap-main/packages/snap/src/db/index.ts:28 |
| Business Impact | Unused functions needlessly increase the size of the snap and reduce code readability. Critical readers may also interpret them as “sloppy” and unprofessional. |
Description
db/index.ts contains an unused function: set(string, any).
set(string, any):
async set(key: string, value: any) {
const newState: any = {};
newState[key] = value;
return await snap.request({
method: 'snap_manageState',
params: { operation: 'update', newState },
});
}
Mitigation
We recommend that you remove the specified function in production environment.
Misleading Error
| ID | SAY-06 |
| Status | Fixed |
| Risk | Informational |
| Location | cosmos-metamask-snap-main/packages/snap/src/helpers/parser.ts:81-83 |
| Business Impact | This kind of error message may be useful for debugging during development, but users may find it confusing. |
Description
In tokenToString, if trace is empty after assigning DENOMS[token.denomination] to it, an error message saying “No” is returned.
src/helpers/parser.ts:81-83
if (!trace) {
throw new Error('No');
}
Mitigation
Replace the error with something a bit more descriptive, like “Empty trace”.
Redundant Usage of getMessageDetails()
| ID | SAY-07 |
| Status | Fixed |
| Risk | Informational |
| Location | cosmos-metamask-snap-main/packages/snap/src/helpers/parser.ts:369 |
| Business Impact | Calling the function twice constitutes an unnecessary operation that has very little performance impact, but needlessly clutters the code. |
Description
In parse(any, string, string), the getMessageDetails(), which is called for each message sent in its invocation, returns the appropriate message about the operation to the user. On line 369 the call to this function is duplicated even though its output is already in panelMsg.
Notice how getMessageDetails is called twice:
parsedMessages.forEach((msg) => {
const panelMsg = getMessageDetails(msg.parsed, msg.raw);
if (panelMsg = 'Unknown Transaction Type') {
panels.push(heading(`${getMessageDetails(msg.parsed, msg.raw)}`));
}
});
Mitigation
Use the already assigned panelMsg variable instead of calling the function twice.
Appendix A: Security Evaluation Fixes
After a review by the Sayfer team, we certify that all the above-mentioned security issues have been addressed by the LeapWallet team.
Fixes commit hash: c9ed0cef9b345e01acc628decb7dac24baceb275